
The Scope
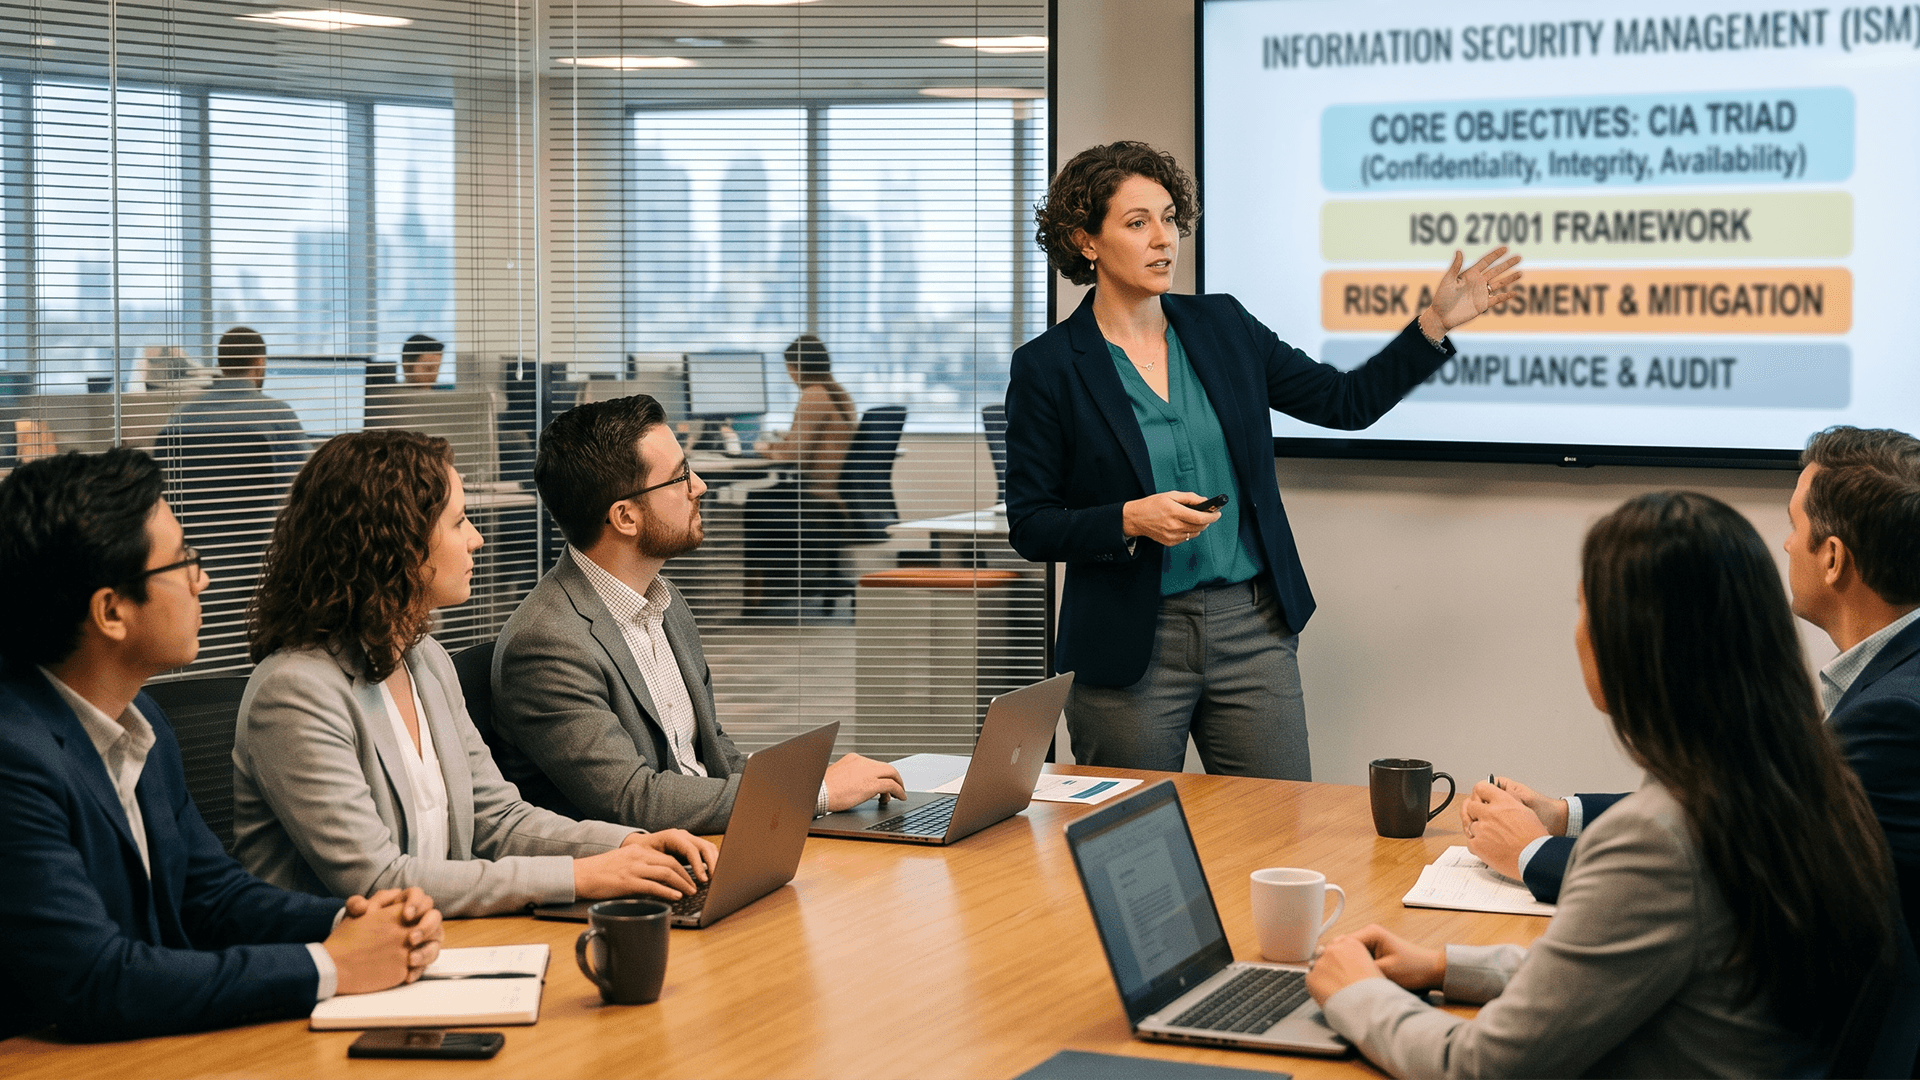
ISO/IEC 27001 certification verifies that an organisation has established, implemented, maintained, and continually improved an Information Security Management System (ISMS) to protect the confidentiality, integrity, and availability of information. The certification provides a systematic approach to managing information security risks and safeguarding information assets against threats, vulnerabilities, unauthorised access, loss, misuse, or disruption.
The standard applies to all forms of information, whether digital, physical, intellectual, cloud-based, outsourced, or internally managed, helping organisations strengthen information security governance and resilience.
The Standard
This certification is based on:
ISO/IEC 27001 – Information Security Management Systems (ISMS) – Requirements
Information security governance
Information security risk assessment and treatment
Protection of confidential, sensitive, and critical information
Cybersecurity and data protection controls
Access control and user management
Incident management and response
Business continuity and information resilience
Supplier and third-party security management
Security awareness and training
Monitoring, auditing, and continual improvement
The certification assesses the organisation’s ability to identify information security risks and implement appropriate controls to protect information assets throughout their lifecycle.
Who Should Apply
ISO/IEC 27001 certification is suitable for organisations of all sizes and sectors that manage, process, store, transmit, or rely on sensitive information.
The certification is particularly relevant for:
Information Technology Companies
Software Development Organizations
Cloud Service Providers
Data Centers
Financial Institutions and Banks
Insurance Companies
Healthcare Organisations
Government and Public Sector Entities
Telecommunications Providers
Professional Services Firms
E-Commerce Companies
Manufacturing Organisations
Educational Institutions
Logistics and Transportation Companies
This certification is ideal for organisations seeking to strengthen information security, protect sensitive data, manage cybersecurity risks, comply with regulatory requirements, enhance stakeholder confidence, improve business resilience, and demonstrate a commitment to internationally recognised information security best practices.